
Agent accountability interview: governance is a document until identity enforces it
Most enterprise AI governance is written down and not enforced. In this agent accountability interview, Thomas Chen argues the fix is the one used for connected devices in the field: bind every action to an accountable identity, enforce the rule at the point of use, and keep the personal data out of it.
nxtlinq and IKE Tech
nxtlinq, which Thomas founded, works on AI security and governance, with a portfolio he describes as about six patents in AI and identity. IKE Tech is a joint venture he helped form, applying tokenized identity to identity and compliance infrastructure for regulated products.
The relevance to this agent accountability interview is the transfer. Enforcing a rule on a physical device at the point of use — where a device, a user and a regulator meet — is a solved-enough problem. The claim is that the same discipline applies to software agents, and that without it governance remains a document.
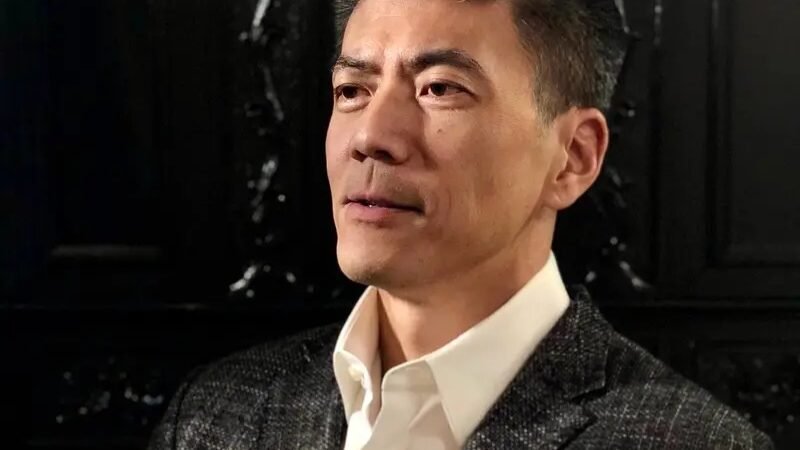
Thomas Chen
Thomas Chen is a co-founder of Berify and founder of nxtlinq, and one of the parties behind the IKE Tech joint venture. He brings more than 25 years in cybersecurity and compliance, and his recent work centres on identity and compliance infrastructure for regulated products using tokenized identity — enforcing rules at the point of use without storing personal data.
His argument in this agent accountability interview is that most enterprise AI deployments treat identity as a login problem, when it is an architecture problem. Policy alone does not enforce compliance; technology has to. And the same principle that governs a connected device in the field applies to an AI agent: without identity-bound accountability, autonomous decisions cannot be audited, and governance stays a document rather than a control.
He is also willing to discuss where decentralised identity architectures fall short, which is the part of this conversation most worth having. Readers will come away with a clearer view of what an agent’s accountable identity actually contains, what enforcement at the point of use requires, and why so many agent pilots never reach production governance.
—
Policy versus enforcement
Q1. In one sentence: what does “policy alone does not enforce compliance” mean when the actor is an AI agent rather than a person?
TC: A written policy can tell an AI agent what it should do, but only technology can enforce those limits at the moment the agent acts. Without that enforcement, nothing stops the agent from doing what it should not.
Q2. Where exactly does technology have to take over from policy — what is the handoff point, and what is still legitimately left to a written rule?
TC: Policy establishes the rules. Technology takes over when an agent attempts to execute an action, such as accessing data, calling an API, transferring funds or delegating work to another agent. That is the point where authorization must be verified before the action is allowed. Written policy still defines acceptable use, risk tolerance, accountability and exceptions. Technology translates those rules into permissions that can be enforced.
Going one step further, an agent’s permissions should travel with its identity, not sit in a separate policy repository that the agent is trusted to consult at every step.
Identity-bound accountability
Q3. What does an accountable, auditable identity for an agent actually consist of — what fields, what issuer, what verification?
TC: An agent needs more than a name or an API key. It needs a verifiable identity tied to who deployed it, what it is authorized to do, how long that authority lasts and who can revoke it. In practice, that means a unique identifier and cryptographic public key issued by a trusted authority, the responsible organization and any verified human sponsor, and an authorization scope carried with the identity. It also means a defined lifecycle of issuance, expiration, revocation and status, backed by a tamper-evident record of what the agent did.
Agent Acts Wrongly
Q4. When an agent acts wrongly, who is accountable — the deployer, the builder, or the identity holder — and how does identity resolve that in practice?
TC: Identity does not automatically determine legal liability. What it does is establish a verifiable chain of responsibility: who deployed the agent, who authorized its action and what it actually did. The builder may be responsible for a design defect. The deployer may be responsible for granting excessive permission. The person or organization that authorized a task may be responsible for the instruction or approval it gave. Identity-bound execution helps distinguish among those situations through verifiable evidence.
To me, accountability starts with whoever authorized the action in the first place, because you cannot establish meaningful accountability without knowing that. This is where many enterprises have a gap. Most use a mix of platforms, and identity tokens often do not carry across them. When an agent starts calling tools and spawning sub-agents, the trail back to the authorizing human can break. That is why traceability to the origin matters and why the evidence record must be tamper-evident.
Tokenized identity
Q5. Tokenized identity lets a system verify who or what is acting without retaining personal data. Walk us through what is actually stored, what is not, and what a verifier can and cannot learn.
TC: The idea is to separate proving identity from repeatedly exposing personal information. A trusted identity provider verifies the human. The system then issues a cryptographically verifiable credential, or token, that is used for later authorization in place of the underlying personal information.
– What is stored: the token itself, its issuer, its validity and status, the authority it conveys and records of activity.
– What is not stored or shared: the raw personal information behind the verification. A verifier does not automatically receive it.
– What a verifier can learn: that the credential is valid, who issued it and what authority it conveys.
There is a limit. Pseudonymous identifiers and activity records can still reveal patterns or become linkable over time, so privacy requires careful architecture, not just tokenization. The goal is to verify authority without unnecessarily exposing the person behind it.
Model has Limits
Q6. You have offered to discuss where that model has limits. Where does it break — and what class of decision can it not cover?
TC: Identity and authorization can establish whether an agent is permitted to act. They cannot guarantee that the decision the agent makes is correct, ethical or safe. An agent might be properly authorized to review a loan application, but that does not mean its recommendation is accurate or free of bias. This is the difference between probabilistic and deterministic systems. Identity controls do not independently prevent hallucinations, flawed reasoning or every form of malicious behavior. Those risks require additional safeguards, including evaluation, monitoring, data controls and human oversight. Authorization is not the same as correctness, and you need both.
Point of use
Q7. You have enforced rules at the point of use in the physical world. What transfers to agents, and what does not survive the move into software?
TC: What transfers from physical devices to AI agents is the principle that verification alone is insufficient. With IKETech, we learned that authorization must be enforced at the point of use, not merely when someone first establishes their identity. A device must respond appropriately when authorization expires, connectivity is interrupted, or access is revoked. AI agents introduce an even greater challenge because they operate continuously, access multiple systems, and delegate tasks to other agents. The same enforcement principle applies, but the number of execution points and security boundaries increases dramatically.
Physical Deployment
Q8. What did that physical deployment teach you that software teams consistently get wrong?
TC: Verification and enforcement are two different things. Many systems verify identity well at the start and then assume authorization stays valid afterward. Building device-level age assurance meant accounting for disconnected devices, expired credentials, interrupted Bluetooth communication and changes in authorization. The same problems exist with AI agents. An agent may begin with legitimate permission but keep operating after its task has changed, its authorization has expired or an operator has revoked its access. A successful login does not mean every action afterward should be trusted. That lesson connects device-level age assurance to the governance of agentic AI.
Agent Lifecycle
Q9. Agent lifecycle from deployment to retirement — what does governance look like at each stage, and why do most pilots fail to reach production governance?
TC: Governance has to cover the entire lifecycle, not just the moment an agent is created or first authenticated. We spent approximately a year developing and testing our agent governance approach, and one lesson became clear: demonstrating that an agent can complete a task is relatively easy. Demonstrating that the same agent can operate safely across enterprise systems, within continuously enforced permissions and with a verifiable audit trail, is considerably harder.
It starts with registration, where the agent’s identity, owner and intended purpose are established. At deployment, the agent is assigned its scope, permissions, credentials and operating boundaries. During execution, authorization is validated before any protected action, and the evidence is recorded. When agents delegate work to sub-agents, governance has to ensure those sub-agents cannot exceed the authority granted to the original agent. Throughout operation, monitoring watches for policy violations, unusual behavior and changes in authorization. Finally, at retirement, credentials are revoked, access is terminated and the required audit log is preserved.
Pilots struggle because showing that an agent can complete a task is now relatively easy, and we built plenty of those demos ourselves. Proving that an agent can operate safely under controlled permissions across enterprise systems is much harder. A demo proves an agent can work. Production governance proves it can be trusted to operate.
Putting to the test
Q10. Where do decentralised identity architectures fall short for agents — is it latency, key management, revocation, or something more fundamental?
TC: Traditional identity and access management was largely designed around human users, applications, and predefined roles. AI agents introduce a different challenge: they can autonomously select tools, delegate tasks, interact with multiple systems, and execute actions faster than a human can supervise. A valid identity credential tells us who or what is acting, but it does not establish whether each action remains within the original authorization. That requires runtime enforcement and a verifiable chain of delegated authority.
Class of Agent
Q11. What would prove you wrong — is there a class of agent where identity-bound accountability is impractical and should not be attempted?
TC: Not every AI interaction needs a full identity and authorization framework. An agent summarizing public information is very different from one accessing confidential records or moving money. For low-risk, isolated applications, extensive identity infrastructure can add unnecessary complexity, and a simpler signature-based identity may be enough. When an agent crosses security boundaries, accesses sensitive information, executes transactions or acts on behalf of people, identity-bound accountability becomes critically important. I would also distinguish between requiring every agent to have an independently issued identity and requiring every consequential action to be attributable to a responsible principal. The second is the more fundamental security objective.
Q12. A team deploying agents this quarter: what is the first thing they should build, and the first thing they should stop doing?
TC: Build an authorization layer between your agents and the systems they can access, one that defines specifically what each agent can reach. Stop treating an API key or a successful login as permission to do everything afterward. In my experience, many organizations are being pushed by executive teams or boards to deploy agents quickly and show results. Many teams are not familiar with the risks, so they apply human authorization, identity and access models to agents. That is the wrong model.
TechRecast Analysis (The Recast)
The Shift in Context — Enterprise AI governance currently lives in frameworks, policies and review boards — artefacts that describe intent and cannot stop an action. Agents act continuously and at machine speed, which makes a document an inadequate control. The shift proposed here is from describing rules to binding them to an identity and enforcing them at the moment of use. That is where this agent accountability interview sits.
Why This Interview Matters — The identity question has been discussed mostly as a design ideal: trust profiles, continuous authorization, verifiable credentials. This conversation is about enforcement — what actually stops an action, and what record remains. That is a narrower and harder question, and it is the one that decides whether governance is real.
Technology Perspective — The technical crux is that accountability needs a subject. An audit trail is only useful if each entry resolves to an entity that can be held responsible, and a token that carries authorisation without carrying personal data is the mechanism proposed. The hard parts are revocation and staleness: an identity that cannot be revoked quickly is worse than none, and a token that outlives its authorisation is a standing permission. Decentralised architectures make revocation harder, which is why his willingness to discuss the limits matters.
Business and Market Perspective — The commercial logic is that regulated sectors cannot adopt agents without an audit story their regulator accepts. That makes identity infrastructure a precondition for the market rather than a feature within it — and it explains why the physical-goods experience is relevant, because regulated products have been through this before.
Leadership Perspective
A practitioner who has shipped authentication at physical scale and now applies it to agents is reasoning from precedent rather than analogy. The relevant lens is whether the transfer is genuine or whether the metaphor is carrying more weight than the mechanism, which the “what does not survive the move into software” question tests.
The Counterpoint — A fair sceptic would argue that blockchain-backed identity adds operational complexity and latency for a problem that conventional PKI and short-lived credentials already address; that “enforce at the point of use” is easier to say than to instrument inside an agent’s reasoning loop; and that three entities and a joint venture make it hard to see what is actually deployed. On this view, the principle is sound and the specific architecture is unproven. This is the strongest opposing case and deserves a direct answer.
What Comes Next — Watch three signals: whether agent identity becomes a procurement requirement in regulated sectors, whether revocation latency becomes a published metric, and whether decentralised identity approaches survive contact with enterprise key management.
Industry Outlook — If Chen is right, agent governance converges on identity-bound enforcement and the policy document becomes a specification rather than a control. If he is wrong, governance stays documentary and agents are confined to low-consequence work.