
AI compliance for small business interview: how Ops Intel’s Scott Neve turns vendor promises into a written record
Most small businesses buy an AI tool and let staff use it without a written policy. In this AI compliance for small business interview, Ops Intel’s Scott Neve explains where that breaks — and what an insurer or auditor will ask for when it does.
Ops Intel
Ops Intel is a company that writes AI compliance frameworks for small and medium businesses. It works across the UK, EU, US, Canada, the Middle East, the Far East and Australasia, publishing frameworks that show how small businesses map their tools against rules such as the EU AI Act, UK GDPR and US state AI laws.
Its focus is deliberately unglamorous. Most AI advice for small businesses is about which tool to buy; Ops Intel’s premise is that the harder question is what a business can prove about the tool afterwards — what data went in, where it went, and who approved it. That is the paperwork layer of AI adoption, and it is where the exposure actually sits.
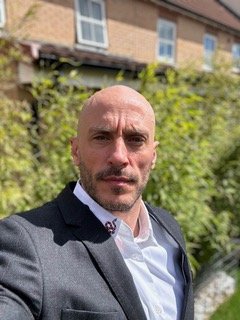
Scott Neve
Scott Neve is the founder of Ops Intel which writes AI compliance frameworks for small and medium businesses worldwide. Before founding the company he spent twenty-five years in sales — an unusual background for a compliance business, and a useful one: the argument he makes is less about regulation than about what a business can actually show when it is asked.
His claim is specific. Most small businesses buy an AI tool and let staff use it without a written policy, and that is where things break: when an insurer or auditor asks what data went into that chatbot, the business has no record. This AI compliance for small business interview tests that claim against the three failure modes he names — supplier terms that quietly let customer data feed public models, staff training that never covers where data goes, and companies treating AI like ordinary software rather than something that needs an incident plan and a central record of use.
Neve frames the core problem as the gap between what software vendors promise and what a business actually needs to write down to stay safe. Readers will come away with a clearer view of how to read supplier terms, what a central record of AI use should contain, and how a small business maps its tools against the EU AI Act, UK GDPR and US state AI laws without a compliance team.
—
The missing record
Q1. In one line, what actually breaks when a small business lets staff use an AI tool without a written policy?
SN: The business loses track of where its customer data has gone, and it cannot get that track back after the fact.
Q2. When an insurer or auditor asks what data went into a chatbot, what should the business be able to produce — and almost never can?
SN: Four things: Which tools were in use and on which accounts, what kinds of data were allowed into each one, what’s the supplier’s terms said about keeping and training on that data at the time, and who signed off on the tool being used. The one they almost never have is the account record. Staff sign up to the free version with a personal email, so the business cannot even say which conversations exist, let alone what was in them. A business account under the firm’s control is the first step to having anything to show.
Vendor promises versus reality
Q3. What is the gap between what software vendors promise and what a business actually needs to write down to stay safe?
SN: A vendor promises things about its own product. Encryption, security certificates, a setting to switch off training. None of that says how your staff use it. The vendor cannot write down which of your clients’ data is allowed into the tool, who approved it, what happens when someone pastes in something they shouldn’t, or who checks the output before it goes to a customer. Under data protection law, the business deciding why and how personal data is used stays responsible for that decision. Buying a tool does not hand that responsibility to the supplier.
Q4. How should a small business read supplier terms to find out whether its customer data feeds a public model?
SN: Look in three places, not just the main terms. First, the privacy policy or data use page for words like “improve our services”, “train”, or “model improvement”. That is where it is said, if it is said at all. Second, check which plan the promise applies to. Business and enterprise tiers often carry different terms from free and personal versions staff actually signed up to. Third, the data processing agreement, for how long inputs are kept, which subprocessors see them, and where the data is stored. If the answer depends on a setting, write down who switched it off and when, because the terms change and the settings get reset.
The three failure modes
Q5. Of the three — unchecked supplier terms, staff training that misses data flows, AI treated like standard software — which is the most common, and which is the most dangerous?
SN: The most common is unchecked supplier terms, because almost nobody reads them before the first person signs up. The most dangerous is trademarking like standard software. Standard software does the same thing every time, and you test it once. AI tools give different answers to the same question, change when the supplier updates the model, and can be talked into things. A business that files AI under “IT” has no incident plan and no record for it. So when something goes wrong, there is nothing to fall back on.
Q6. What does staff training actually need to cover about where data goes, concretely?
SN: Five things, with real examples from their own job rather than slides about AI in general. Which tools are approved and on which accounts, which types of data never go into any AI tool—client personal details, health information, anything under a confidentiality agreement. What happens to what they type, meaning whether it is stored, for how long, and whether it can be used for training. That the output has to be checked by a person before it reaches a client. And who to tell straight away when something has gone in that shouldn’t have. That last one matters most because a mistake reported in an hour can be contained, and one found a month later usually can’t.
Mapping to the rules
Q7. How do you map a small business’s AI tools against the EU AI Act, UK GDPR and US state AI laws without a compliance team?
SN: Start with a list, not the law. Write down every AI tool in use, what it is used for, and what data it goes in. Then ask three questions of each tool.
Does it touch personal data? If yes, data protection law applies wherever you are, including UK GDPR.
Is it used to make decisions about people? Such as hiring, lending, or access to services? That is where most of the specific AI rules bite. Recruitment and credit scoring are high risk under the EU AI Act, and several US states regulate automated decisions about people.
Does it talk to the public or produce content? Then disclosure duties may apply. For example, the EU AI Act transparency rules.
Most tools in a typical office answer yes to the first question and no to the other two, which keeps the work manageable.
Regimes Diverge
Q8. Where do those regimes genuinely diverge, such that one policy will not cover all of them?
SN: Three places. First, the EU has an AI-specific law and the UK does not. The UK regulates AI through existing law, mainly UK GDPR. So the same tool is governed by different rules either side of the channel. Second, the timing differs. The EU AI Act applies in stages. The prohibited practices from February 2025. The transparency duties from August 2026, and the high-risk obligations for things like recruitment and credit scoring from December 2027. Third, the US has no federal AI statute, so it does state by state. Colorado’s rules on automated decisions take effect in January 2027.
New York City already requires bias audits of automated hiring tools, and Utah requires a business to tell a customer they are dealing with generative AI if the customer asks. One set of principles can sit across all of them. One set of procedures cannot. We keep the dates for every market, each checked against its source, on one free page www.opsintel.io/ai-compliance-deadlines
Incident plans and central records
Q9. What does an AI incident plan look like for a small business, and what should trigger it?
SN: One page. Who is in charge, who they call, and what gets written down. The triggers are: personal or confidential data going into a tool it shouldn’t have; AI output reaching a client or the public with something wrong or harmful in it; an AI tool making or influencing a decision about a person that turns out to be wrong; and a supplier announcing a breach or a change of how it uses your data. The first hour is about stopping it and recording what happened. Then comes the legal question. If personal data is involved, a UK or EU business may have 72 hours to report it to the data protection regulator, and that clock starts when you become aware of the breach, not when you finish investigating it. At Ops Intel, it is one of the standard documents in every AI policy we write.
Q10. What belongs in a central record of AI use, and how do you keep it current?
SN: For each tool, its name and supplier, the account type, who owns it inside the business, and what it is used for. What data is allowed in and what is banned. Where the supplier’s terms say the data goes. The date someone last checked those terms, and whether it is used in any decision about a person.
Keeping it current takes two habits. No new tool gets used until it is on the list, so the list is the approval. And then you’ve got to review it every quarter, plus whenever a supplier emails about changed terms, because those emails are the ones nobody reads.
What to do first
Q11. If a small business can only do one thing this month, what should it be?
SN: Find out which AI tools your staff are actually using. Ask them directly and make it clear nobody is in trouble. The honest answer will always be longer than the one management expected, and every other step depends on that list.
Putting the thesis to the test
Q12. What would prove you wrong — is there a case where no written policy is genuinely fine?
SN: A one-person business using AI only on its own material, with no client data, no personal data and no decisions about anyone, probably doesn’t need a formal policy. Drafting your own marketing copy is an example. A short note to yourself about which tools you use and what you never put in them is enough. The case falls apart the moment there is a second person or a client’s data, because then you need a shared rule, not one held in someone’s head.
Q13. What is the strongest argument against formalising AI compliance for small businesses, and how do you answer it?
SN: The strongest argument is that a policy nobody reads is worse than no policy. It costs time, gives false comfort, and gets copied from a template that has nothing to do with how the business works. That is a fair criticism of bad policies, not of having one. The answer is to keep it short and tight to the tools actually in use, and to make the record the main thing. When an insurer, a client or a regulator asks what happened, a record kept in the ordinary course of business is the evidence. A good intention you never wrote down is not. That is how we approach it at Ops Intel: short, specific to the tools in use, with the evidence record alongside the policy.
TechRecast Analysis (The Recast)
The Shift in Context
AI adoption at small businesses has run ahead of AI governance at small businesses. Tools are bought on a card, used by staff within days, and never documented. The compliance frameworks written for large enterprises assume teams, budgets and legal counsel that a ten-person firm does not have. This AI compliance for small business interview sits in that gap.
Why This Interview Matters
The claim is not that regulation is coming — it is that the exposure already exists, and shows up first as an insurance or audit question rather than a fine. That reframing is useful: it makes compliance a practical matter of records rather than a legal abstraction, and it is testable against what a business can actually produce.
Technology Perspective
The technical crux is data flow. Whether customer data reaches a public model depends on supplier terms and configuration, not on the tool’s marketing. The interview should press on the mechanics: what to look for in the terms, what configuration changes the answer, and what a defensible record of use looks like.
Business and Market Perspective
The commercial logic is that compliance is becoming a purchasing condition — insurers, enterprise customers and auditors all ask. A small business that cannot produce a record loses contracts and cover before it ever meets a regulator. That is a market force, not just a legal one.
Leadership Perspective
Neve’s twenty-five years in sales is the relevant lens. He is arguing that the gap between the promise and the record is where risk lives — which is a salesperson’s insight applied to compliance, and it explains why the framing is about what you can show rather than what the law says.
The Counterpoint
A fair sceptic would argue that most small businesses face no realistic enforcement, that formal frameworks are overhead they cannot afford, and that the practical risk is dwarfed by ordinary operational failures. On this view, AI compliance is a product looking for a problem at the small end of the market. This is the strongest opposing case and deserves a direct answer.
What Comes Next
Watch three signals: whether insurers and enterprise buyers start requiring AI-use records as a condition of doing business, whether the EU AI Act’s obligations cascade down to small suppliers, and whether “central record of AI use” becomes a standard artefact rather than a specialist one.
Industry Outlook
If Neve is right, AI compliance becomes a normal small-business discipline — records, incident plans, supplier checks — driven by insurance and procurement rather than regulators. If he is wrong, it stays a niche service for firms that happen to be asked, and the rest carry the risk unrecorded.
Key Takeaways
1. Small businesses adopt AI tools faster than they document them, and the gap is where exposure sits.
2. The first question is usually an insurer’s or auditor’s — what data went into the tool — not a regulator’s.
3. Three failure modes dominate: unchecked supplier terms, staff training that misses data flows, and AI treated like ordinary software.
4. Whether customer data reaches a public model depends on supplier terms and configuration, not on the marketing.
5. Mapping tools against the EU AI Act, UK GDPR and US state laws is possible without a compliance team, but the regimes genuinely diverge.